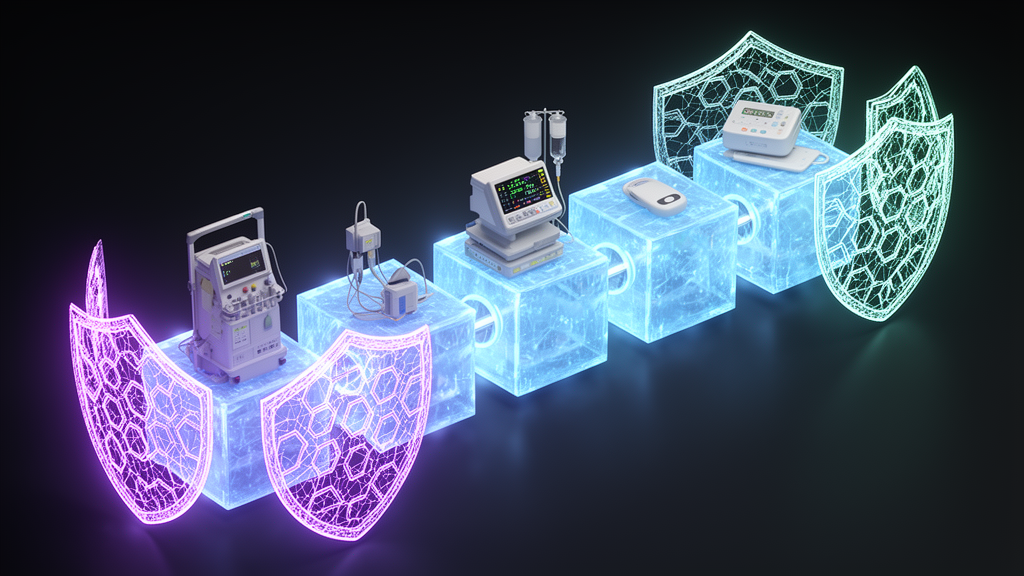
Researchers have unveiled a security framework for the Internet of Medical Things (IoMT) that weaves together software-defined networking, blockchain technology and post-quantum cryptography into a single architecture designed to withstand both today’s cyberattacks and the threats expected once large-scale quantum computers arrive. The framework, described in a study published in Discover Internet of Things, extends the conventional three-plane design of software-defined networking (SDN) with two additional security planes: a Blockchain Plane for decentralized identity verification and a Quantum Security Plane for quantum-safe key establishment.
The motivation comes from a gap the authors identify across existing research. Current SDN-blockchain systems for healthcare networking still rely on ledgers that grow indefinitely, creating storage burdens for resource-constrained medical devices. Post-quantum security proposals, meanwhile, tend to simply swap classical ciphers for quantum-resistant ones without extending the network architecture itself, and many blockchain authentication schemes still depend on centralized certificate authorities. The new framework addresses all three shortcomings at once, according to the study, by combining a self-mutable blockchain, an extended SDN architecture and a lightweight identity scheme based on signed universally unique identifiers (UUIDs).
The self-mutable blockchain is the framework’s central innovation. In conventional blockchain deployments, every authentication record is stored permanently, so the ledger expands without limit. In the proposed design, each authentication block carries an embedded expiration timestamp alongside its hashed UUID, creation timestamp, hash of the previous block and digital signature. Once the current system time reaches the expiration timestamp, every participating node independently and deterministically deletes the block from its local copy of the ledger. Because all honest nodes evaluate the same rule against the same immutable metadata, they reach identical decisions without administrators or additional consensus rounds, preserving the decentralized consistency and tamper resistance of the chain while preventing the accumulation of obsolete credentials.
The authors argue that tampering with this process is computationally impractical. An attacker who tried to alter an expiration timestamp or delete a block early would change the block’s hash, invalidating its digital signature, and the inconsistency would be detected during validation by other nodes, which would reject the modified state. Expired blocks, meanwhile, are useless for future communications, so their removal also helps guard against replay attacks while keeping storage requirements bounded over time.
Authentication in the framework dispenses with certificate authorities altogether. Each IoMT device holds a unique UUID that it digitally signs with its private key. When a sender transmits a message, the recipient verifies the signature, decrypts the payload, hashes the UUID with its timestamp and checks whether the corresponding entry exists on the distributed blockchain. If a majority of blockchain nodes confirm the entry, the sender is authenticated; if not, the message is ignored. Message encryption relies on Kyber, a lattice-based key encapsulation mechanism selected by the US National Institute of Standards and Technology as a post-quantum standard, which protects against adversaries running Shor’s or Grover’s algorithms and against harvest-now-decrypt-later attacks in which encrypted data is collected today for decryption once quantum computers mature.
The extended SDN architecture separates these security functions from ordinary network control. The application plane remains unchanged, hosting traffic engineering and policy enforcement, while the control plane coordinates interactions with the two new planes. The Quantum Security Plane handles all post-quantum cryptographic tasks, including Kyber key encapsulation and optional integration with Quantum Key Distribution (QKD), which exchanges keys using the quantum properties of photons and can detect eavesdropping through the disturbance it causes in quantum states. The Blockchain Plane manages decentralized identity verification and the signing of UUID records. This modularity, the authors write, improves scalability and makes security policy management easier than bundling such functions into the control plane itself.
To test the design, the team built a simulated SDN environment using Mininet and the Ryu controller, with OpenFlow switches standing in for IoMT devices, a permissioned blockchain, Kyber for key encapsulation, AES for symmetric encryption and SHA-256 for authentication hashes. Across multiple simulations, the framework achieved an average authentication latency of 28.4 milliseconds and an average communication overhead of 23.6 kilobytes per authentication transaction. Average blockchain storage overhead was held at approximately 13.2 megabytes, which the authors attribute to the self-mutable scheme’s removal of expired authentication records. Block creation, verification and deletion took an average of 5.4, 2.3 and 2.8 milliseconds respectively, and the system sustained an average throughput of 156 authentication transactions per second while managing up to 100 simulated IoMT devices simultaneously.
Formal security analysis supplemented the performance testing. A BAN logic analysis, which models the beliefs that honest participants can derive from protocol messages, concluded that the receiver can correctly believe the sender sent both the signed identifier and the message. The protocol was also modeled in HLPSL and verified with the AVISPA tool using both the OFMC and ATSE backends, both of which reported the protocol as SAFE, finding no attack traces under bounded session assumptions for the goals of sender and receiver authentication, message confidentiality, integrity of sender identity through blockchain hash validation, and resistance to impersonation. The authors note these results hold under bounded session assumptions, and the analysis assumed a Dolev-Yao adversarial model in which attackers can eavesdrop, manipulate, replay, delay or insert traffic but cannot compromise a large number of blockchain validation nodes or break the security assumptions of Kyber.
Benchmark comparisons of encryption algorithms in the study showed AES maintaining consistently low and stable encryption and decryption times across file sizes from 0 to 300 kilobytes, outperforming both DES, whose times rose steadily with file size, and RSA, which showed higher and more variable key generation and decryption times due to its computationally intensive asymmetric operations. The authors also report that the proposed protocol’s worst-case time complexity is O(n + b + 1), with cryptographic operations running in constant time and broadcast and verification costs proportional to the number of blockchain nodes, which in permissioned healthcare deployments typically number five to ten validators. In their comparison against other recent authentication schemes, they report the framework attains comparatively low authentication and communication costs through lightweight blockchain-based signature verification of UUIDs, while the self-mutable design limits ledger growth over time.
The framework is not yet proven outside the laboratory. The authors state plainly that the solution has been tested only within an SDN simulation environment and has not been deployed on large-scale physical IoMT testbeds, and they caution that synchronizing geographically dispersed blockchain nodes may introduce delays in very large implementations. Real-world deployment would also need to address the computational expense of quantum-safe algorithms, standardization of interfaces between classical and quantum systems, compliance with healthcare privacy regulations such as GDPR and HIPAA, and interoperability across diverse medical devices. Future work, they write, will focus on implementing the framework in practical hospital networks, testing large-scale IoMT deployments, optimizing the self-mutable blockchain for low-power medical devices, and benchmarking additional NIST post-quantum algorithms. The study was published as open access on 17 October 2026.
Subject of Research: A quantum-resilient SDN and blockchain framework for securing Internet of Medical Things communications
Article Title: A quantum-resilient, blockchain-enabled SDN framework for securing IoMT systems
Article References: Shrestha, S., & Roy, K. S. (2026). A quantum-resilient, blockchain-enabled SDN framework for securing IoMT systems. Discover Internet of Things, 6(1), Article 216. https://doi.org/10.1007/s43926-026-00498-1
Image Credits: AI Generated
DOI: 10.1007/s43926-026-00498-1
Keywords: Internet of Medical Things, software-defined networking, blockchain, post-quantum cryptography, Kyber, quantum key distribution, self-mutable blockchain, cybersecurity, healthcare, authentication, AVISPA, BAN logic
News Source: Katie Riggs. (October 28, 2026). Blockchain and quantum-safe cryptography combine in new framework to secure medical device networks. Scienmag.