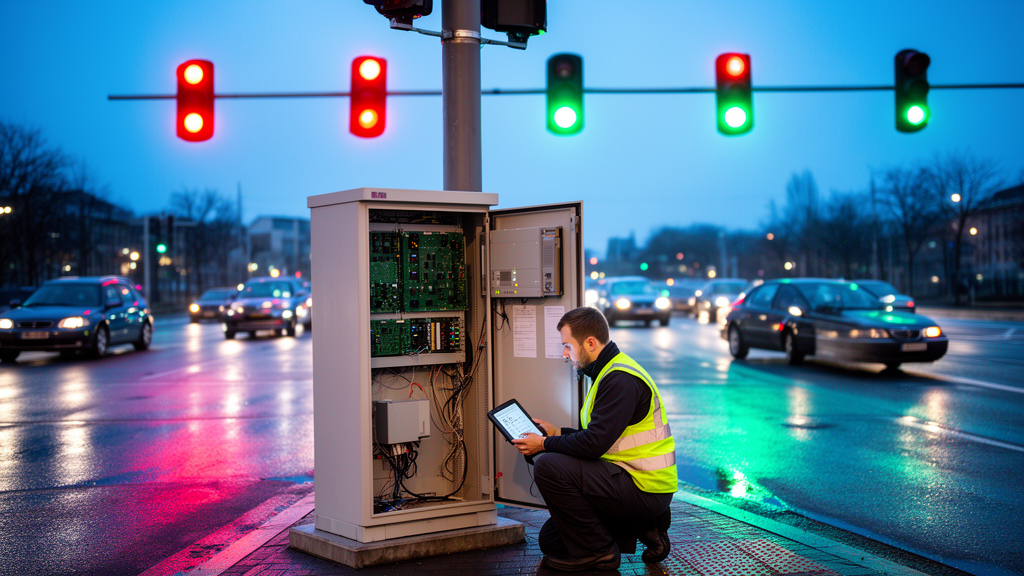
Traffic lights have quietly become computers on street corners, and that means they can be hacked. A new study presents GuardBox, a detection framework that watches an intelligent traffic signal controller from several angles at once—its phase timing, the commands flowing to it, and the physical sensors inside its roadside cabinet—to catch cyber-physical attacks before a manipulated intersection turns into a corridor-wide jam. The work, published in Discover Computing, was tested entirely in simulation, but its authors argue the underlying principle, that no single telemetry channel can catch every attack family, applies directly to real deployments.
The motivation comes from a well-documented security record. The Green Lights Forever study showed that deployed traffic infrastructure could be manipulated with commodity radio equipment and weak protocol protections, and automotive security research has repeatedly demonstrated that networked embedded controllers can expose safety-relevant actuation paths. A malicious command to a signal controller is not just a software event: it can alter signal timing, create unsafe queues, increase emissions, delay emergency vehicles, or mask a physical break-in to the controller cabinet. Existing defenses such as network segmentation, hardening, and logging are necessary, but they leave a harder problem unsolved—once something abnormal is detected, an operator still needs to know what kind of attack it is, because the right response differs sharply between a replayed command stream, a tampered timing plan, and someone prying open a cabinet.
GuardBox addresses that attribution problem with a deliberately multimodal design. An LSTM autoencoder, a recurrent neural network trained only on normal telemetry, models the expected temporal behavior of the controller and flags windows whose reconstruction error leaves the learned-normal envelope. Alongside it, a random forest classifier assigns each telemetry snapshot to one of five operational classes: normal, timing manipulation, replay attack, physical intrusion, or combined cyber-physical attack. The authors chose the random forest for its interpretable feature importances, its handling of mixed feature types, and calibrated class probabilities, not because it was uniquely accurate. The two components complement each other: the autoencoder supplies a class-agnostic novelty signal, while the classifier maps evidence to a specific, response-aligned label.
The feature engineering is central to the whole approach. The collector records eighteen features per five-second snapshot, spanning controller behavior such as phase deviation and elapsed time, command-channel activity such as command counts and command-rate delta, traffic and emission variables, and physical cabinet sensors including door state, vibration, temperature, and power-supply voltage. Notably, the LSTM reconstructs only the thirteen behavioral, command, and traffic features, deliberately excluding the five sensor features so that a physical intrusion—which leaves controller behavior untouched—is detected by the sensor channel rather than by temporal reconstruction.
The evaluation ran in a SUMO traffic-simulation testbed of nine signalized intersections, with attacks injected internally by the collector for reproducibility. Across 375 held-out scenarios—75 per class—GuardBox detected timing manipulation, replay, and combined attacks in every single scenario, a 100 percent detection rate for each, and produced zero false positives on 75 normal-operation scenarios. Physical intrusion lagged at 81 percent, detected in 61 of 75 cases, and the authors trace this shortfall precisely: the sensor-anomaly alarm is intermittent by design, asserted only when sporadic vibration exceeds a threshold or cabinet temperature exceeds 45 degrees Celsius, so a decision window near attack onset may not accumulate enough flagged snapshots. Extending the rolling window from 12 to 18 snapshots restored physical-intrusion detection to 100 percent at the cost of a small latency increase, confirming the mechanism quantitatively.
The authors are unusually candid about what the near-perfect numbers do and do not mean. Because each attack family is injected by an explicit signature rule, the classes are separable by construction—indeed, even a plain logistic regression reached macro F1 of 1.0 on the same data, and every baseline from support vector machines and XGBoost to a 1D-CNN and a GRU network attributed the attacks with macro F1 of at least 0.9979. The attribution result, they write, is best read as a check that the collector produces the intended, mechanism-aligned signatures and that the classifier recovers them, not as a claim of field-level generalization. Unsupervised baselines behaved differently: a one-class SVM matched GuardBox on the cyber and combined classes and reached 85 percent on physical intrusion, while an isolation forest fired reliably only on combined attacks—but neither emits an attack-family label or severity score, which is where GuardBox’s operational value lies.
Stress tests revealed where the detector is robust and where it is not. Adding Gaussian sensor noise left attack detection essentially unaffected, but the false-positive rate on normal operation was highly sensitive: 0 percent on clean data, 3 percent at moderate noise, but 71 percent when noise reached half a feature standard deviation and 100 percent at full magnitude, a consequence of the tightly calibrated reconstruction threshold. The authors conclude that the threshold must be recalibrated to the field noise floor rather than to clean simulation data. Two benign conditions were also tested: an authorized open-cabinet maintenance visit was never flagged, because the sensor alarm keys on vibration or temperature disturbance rather than the door contact alone, but a brief emergency-preemption phase change was flagged in every case, since a moderate phase deviation is indistinguishable from mild timing manipulation. Separating legitimate preemption from attack, they note, requires supplying the detector with an authorized-event allowlist before any deployment.
Generalization checks across three SUMO networks—a four-intersection grid and a different-demand variant of the nine-intersection grid, each with independently recalibrated thresholds—showed the cyber and combined classes remained at full detection with zero false positives, while physical intrusion tracked the same boundary effect. The authors emphasize this shows the normal-behavior model transfers across networks, not that real attacks would manifest differently in different geometries. On the computational side, a single detection decision takes about 34 milliseconds on a commodity CPU, far below the 5-second snapshot interval, and a containerized deployment running under resource limits below a Raspberry Pi 5 sustained a mean decision time of 42.5 milliseconds at a 0.65-gigabyte memory footprint—evidence that detection could run on cabinet-adjacent hardware.
The framework has clear boundaries. Denial-of-service flooding manifests as packet-rate exhaustion outside the current telemetry and is explicitly out of scope; extending coverage would require packet-rate and connection-state monitoring. A stealthy adversary who keeps each signal just below the detection thresholds could evade the current detector, and adaptive or adversarially trained thresholds remain untested. The random forest can only assign one of its trained labels, so a genuinely novel attack would be mislabeled—though the LSTM channel would still raise an anomaly if the attack perturbs the behavioral or command channels. And because the entire evaluation is simulation-based, field noise, cabinet hardware variation, maintenance events, and adversarial adaptation remain unvalidated; the next step is hardware-in-the-loop testing on a physical NEMA TS-2 compatible controller.
The central lesson the authors draw is a design principle for traffic-signal security monitoring: cyber-only, physical-only, and combined attacks should not be collapsed into a single anomaly label, because the class determines the response—a timing manipulation may require phase reversion, a replay attack command-channel isolation, a physical intrusion a field dispatch, and a combined attack both at once. As signal controllers gain networked management and telemetry interfaces, the attack surface around devices historically built for reliability rather than hostile networks keeps growing. GuardBox offers a template for watching those devices with the same multimodal attention a human operator would need—while honestly acknowledging that simulation-separable signatures are only the first step toward protecting real intersections.
Subject of Research: Multimodal machine-learning detection and attribution of cyber-physical attacks against intelligent traffic signal controllers in a SUMO simulation testbed
Article Title: Multimodal detection of cyber-physical attacks against intelligent traffic signal controllers
Article References: Noman, S. A., & Noman, H. A. (2026). Multimodal detection of cyber-physical attacks against intelligent traffic signal controllers. Discover Computing, 29(1), Article 811. https://doi.org/10.1007/s10791-026-10754-1
Image Credits: AI Generated
DOI: 10.1007/s10791-026-10754-1
Keywords: traffic signal security, cyber-physical attacks, anomaly detection, LSTM autoencoder, random forest, SUMO simulation, intrusion detection, intelligent transportation systems, attack attribution, cabinet sensors, false-positive rate, GuardBox
News Source: Denise Maddox. (October 27, 2026). Research report: Multimodal detection of cyber-physical attacks against intelligent traffic signal controllers. Scienmag.