A simulated blockchain and Internet of Things digital banking framework designed for Nigeria’s financial ecosystem achieved a mean transaction confirmation latency of 1.07 seconds and reached a protocol-level peak throughput exceeding 237,000 transactions per second under controlled conditions, according to research published in Discover Networks. Conducted by Maimunatu Ya’u Ibrahim and colleagues, the investigation assessed whether distributed ledger technology could overcome persistent security and scalability vulnerabilities in developing economies. The researchers evaluated a prototype in a controlled computational environment using Python rather than deploying onto live networks. Their findings indicate that implementing a lightweight Proof of Authority consensus mechanism across permissioned institutional nodes provides consistent one-second block intervals while preserving transactional integrity. By grounding the architecture in Nigeria’s financial landscape, the study presents empirical benchmarks for securing connected devices against cyber fraud and infrastructure failures.
The investigation was driven by structural security risks that distinguish digital financial deployments in developing nations from those in advanced economies. While blockchain systems have expanded across global banking, prior academic models frequently presume reliable connectivity and widespread adoption of modern transport encryption. In Nigeria, the rapid growth of digital banking and Internet of Things payment interfaces has coincided with escalating threats of cyber theft, insider abuse, and weak authentication. Empirical findings cited in the study reveal that over 99 percent of examined Internet of Things servers in comparable environments lack secure protocols such as Transport Layer Security, leaving connected hardware vulnerable to interception and brute-force intrusion. Concurrently, centralized banking infrastructures face systemic single-point vulnerabilities, where internal manipulation or compromised database servers can alter financial records, facilitate fraud, or disable transaction processing across participating financial institutions.
To evaluate existing technological countermeasures, the authors examined an earlier payment framework proposed by Bojjagani and colleagues that utilized elliptic curve cryptography for wearable devices. That system connected smart wristbands, watches, and goggles to a smartphone, coordinating transactions through public key encryption, digital certificates, and certificate authorities. However, Ibrahim and colleagues identified severe computational and operational bottlenecks within that design when applied to developing economies. Wearable devices possess constrained processing power and limited memory, making the execution of complex elliptic curve encryption and Advanced Encryption Standard ciphers resource-intensive and prone to latency. Furthermore, communication across wireless channels like Bluetooth and Near-Field Communication remains susceptible to eavesdropping and man-in-the-middle exploits. Most significantly, relying strictly on point-to-point cryptography fails to prevent insider ledger tampering or mitigate centralized institutional failures, underscoring the necessity of transitioning from isolated encryption schemes to distributed ledger protocols.
The proposed system directly aligns core blockchain mechanisms with the technical vulnerabilities of Internet of Things financial infrastructure. In this architecture, decentralization eliminates single points of server failure by distributing ledger storage across multiple licensed institutions. Cryptographic hashing via SHA-256 enforces strict data immutability, ensuring that any unauthorized alteration of transaction amounts or account records breaks the sequential block hash chain and triggers immediate network rejection. Consensus validation via Proof of Authority establishes rapid verification without the computational overhead of mining or token staking. In addition to ledger defenses, the authors incorporated an endpoint security model to safeguard user devices against physical theft and unauthorized access. Client hardware relies on dedicated Secure Elements for tamper-resistant private key storage, while transaction authorization mandates secondary verification through personal identification numbers or biometric scans. Lost or compromised devices can be revoked at the gateway level, preventing physical possession from compromising funds.
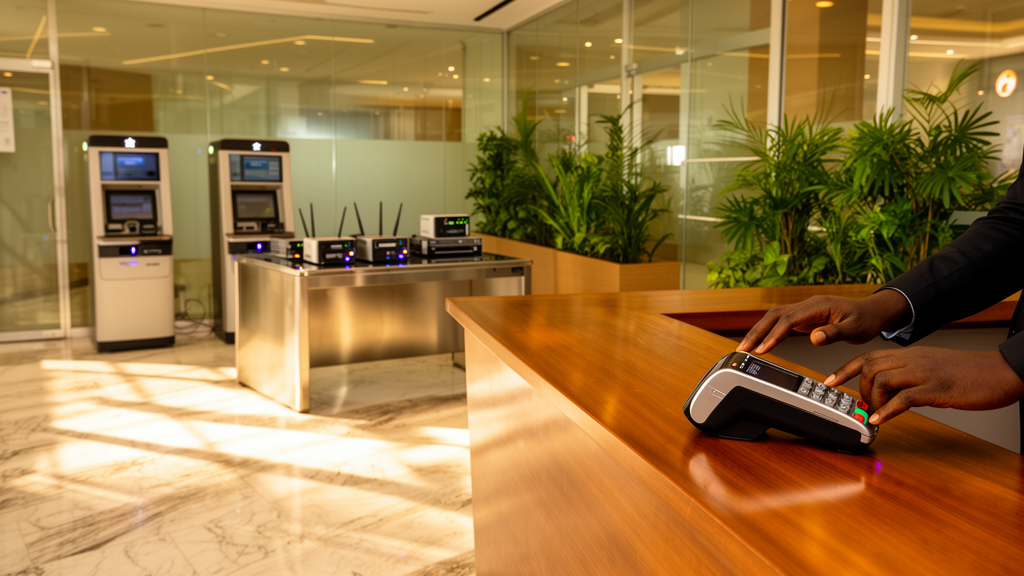
The operational workflow begins when a consumer initiates a payment through an Internet of Things device running an authenticated banking application. The request packages essential metadata, including the transaction amount, merchant identifier, timestamp, and a digital signature generated using an RSA private key. The transmitting device forwards this payload to the customer’s issuing bank, where a payment gateway verifies the cryptographic signature to confirm authenticity and user authorization. Following verification, the transaction enters a pending pool, and the issuing bank aggregates requests into a proposed block cryptographically tied to the preceding block’s hash. The candidate block is broadcast to peer institutions across the permissioned consortium network. Designated validator nodes confirm signature validity, ledger state, and hash integrity under Proof of Authority rules. Once validated, automated procedures execute account adjustments, debiting the customer, crediting the merchant, and appending the validated block permanently to the distributed ledger.
Governance within the framework is specifically structured to align with Nigerian banking regulations rather than open, anonymous network topologies. The architecture operates as a permissioned consortium where node operation is limited to regulated financial institutions, overseen by the Central Bank of Nigeria. In this model, the central bank exercises a dual role, functioning both as regulatory supervisor and supervisory consensus validator to ensure compliance with financial mandates, transaction auditing, and anti-money laundering controls. Commercial banking institutions act as operational validators managing daily transaction flows in their traditional capacities as issuers and acquirers. To prevent institutional collusion, validator cartels, and insider manipulation, the system establishes a formal onboarding process requiring consensus voting and central bank certification. Furthermore, validation privileges are subject to periodic performance audits, activity rotation, and immutable on-chain action logging, ensuring that any collusive behavior or improper block tampering is detectable by peer institutions.
The research incorporates a threat model evaluating potential attacks from malicious merchants, compromised bank servers, rogue validators, and external network adversaries. In traditional environments, dishonest merchants might alter payment totals or deny completed transactions, while compromised bank nodes could selectively censor transfers or attempt double-spending. The proposed architecture neutralizes these vectors through cryptographically enforced immutability and multi-party validation. Because every validated block contains an SHA-256 hash uniquely binding transaction amounts, timestamps, and signatures, retroactive tampering causes detectable ledger inconsistencies across distributed nodes. The Proof of Authority protocol prevents rogue validators from unilaterally approving invalid transactions, as all validation actions are tied to cryptographically authenticated institutional identities subject to administrative revocation. External hackers attempting replay attacks, message eavesdropping, or unauthorized injection are stopped by RSA digital signatures and permissioned network access control, ensuring robust protection without requiring excessive device-side computational resources.
Addressing regulatory constraints, the researchers designed the framework to balance blockchain auditability with data protection mandates established by the Nigeria Data Protection Act and international privacy frameworks. Complete transparency on a replicated ledger poses privacy risks if confidential customer data becomes visible to all participating consortium members. To resolve this tension, the system enforces strict separation between on-chain settlement records and off-chain customer information. Personally identifiable information, customer account balances, and sensitive personal records remain stored securely within internal, bank-controlled databases subject to traditional banking secrecy standards. The shared blockchain ledger records only cryptographic transaction references, pseudonymous public identifiers, and SHA-256 integrity hashes. This selective transparency allows authorized institutional validators to verify transaction authenticity and maintain regulatory audit trails without exposing private customer identities, aligning directly with core legal requirements of data minimization, purpose limitation, and storage limitation.
To evaluate performance, the researchers developed a software simulation using Python 3.10 and executed experimental workloads within a Google Colab computational environment. Cryptographic operations utilized hashlib for SHA-256 hashing and pycryptodome for RSA digital signatures configured with a 2048-bit key length, matching current commercial banking standards while leaving room for future integration of post-quantum algorithms such as CRYSTALS-Dilithium and CRYSTALS-Kyber. Interbank communication flows were simulated using Flask interfaces to emulate interactions between issuer gateways, acquirers, and regulatory validators. The experimental network modeled a 50-node permissioned consortium executing batches of programmatically generated payments across 1000 sequential blocks. In the baseline configuration, each block processed a single transaction to allow precise tracking of confirmation latency and deterministic consensus behavior. Across all experimental configurations, tests were repeated across ten independent trials, with mean values recorded to ensure statistical reliability across varying transaction values and network loads.
The experimental evaluation confirmed consistent latency and high throughput across the simulated network. Using Proof of Authority consensus under the 50-node configuration, the framework achieved a mean transaction confirmation latency of 1.07 seconds, maintaining a narrow variance of plus or minus 0.12 seconds across all trials. Block generation intervals remained stable at one second, experiencing only minor delays of less than 1.3 seconds during intensive stress testing without cascading network disruption. Under continuous execution conditions, the prototype attained a peak protocol capacity of approximately 237,000 transactions per second, substantially outperforming traditional elliptic curve cryptography systems and reported benchmarks for Nigeria’s eNaira infrastructure. In tamper-resistance trials, deliberately injected transaction modifications resulted in immediate hash mismatches, leading validator nodes to reject compromised blocks without corrupting ledger integrity. Furthermore, scaling the node count from 10 to 50 caused less than three percent throughput degradation, demonstrating near-linear scalability.
The authors concluded with a comparative evaluation of consensus mechanisms and an appraisal of study limitations. Contrasting Proof of Authority against Proof of Stake and Practical Byzantine Fault Tolerance, the researchers found that while Practical Byzantine Fault Tolerance achieved high theoretical fault tolerance, its communication overhead escalated exponentially as nodes exceeded 30, creating severe latency bottlenecks. Proof of Stake introduced undesirable latency variability due to validator selection mechanics. Thus, Proof of Authority proved most practical for Nigeria’s digital banking context. However, the authors explicitly noted that their simulation abstracted physical internet latency, bandwidth constraints, and packet loss by executing within a single runtime environment. The reported 237,000 transactions per second throughput reflects upper-bound protocol efficiency rather than achievable wide-area internet performance. Additionally, physical Internet of Things hardware integration and live regulatory interoperability remain conceptual, establishing vital benchmarks and clear directions for future empirical deployment.
Subject of Research: Blockchain and Internet of Things security framework for digital banking in Nigeria
Article Title: A blockchain IoT framework for secure digital banking in Nigeria with simulation and consensus mechanism evaluation
Article References: Ibrahim, M. Y., Musa, K. I., Ahmad, A., & Tella, M. (2026). A blockchain IoT framework for secure digital banking in Nigeria with simulation and consensus mechanism evaluation. Discover Networks, 2(1), Article 9. https://doi.org/10.1007/s44354-026-00025-2
Image Credits: AI Generated
DOI: 10.1007/s44354-026-00025-2
Keywords: blockchain technology, Internet of Things, digital banking, Nigeria financial sector, Proof of Authority, transaction latency, cryptographic hashing, SHA-256, RSA-2048, permissioned consortium, Central Bank of Nigeria, tamper resistance, smart contracts, Nigeria Data Protection Act, Practical Byzantine Fault Tolerance, Proof of Stake, Secure Elements, fintech security
News Source: Denise Maddox. (November 12, 2026). Simulated Blockchain IoT Framework Achieves Low Latency for Nigerian Banking. Scienmag.