Computer systems researchers have introduced a multi-layered defense architecture called the Flexible and Sturdy Memory Integrity Guardian to counter volatile cyberattacks executed directly within operating memory. Documented in an experimental evaluation published in Cluster Computing, the defense framework achieved an aggregate cross-layer anomaly detection F1-score of 93.20 percent across a dedicated enterprise testbed comprising 625 security-relevant nodes. Developed by an engineering team including Jean Rosemond Dora, Ladislav Hluchý, Robert Andok, and Friday Ikechukwu Agu, the system confronts the growing operational challenge posed by memory-resilient payloads. These malicious programs operate within the dynamic random-access memory of ubiquitous productivity software, particularly Microsoft Word and Microsoft Outlook, bypassing conventional security controls. By uniting low-overhead hardware virtualization telemetry with deep learning behavioral analysis, the researchers demonstrated that runtime in-memory monitoring can reliably uncover evasive malware executions that leave no residual static artifacts on physical computer storage drives.
The study investigates an adversarial paradigm shift across modern enterprise environments, where sophisticated malware increasingly migrates from traditional disk-based deployment models to completely volatile in-memory operations. Traditional intrusion workflows followed a doctrine of installing files and persisting on persistent disks, allowing security teams to rely upon static file scanning, disk forensics, and signature-matching databases. In contrast, memory-resident exploits adhere to a philosophy of running and evading, executing transient assembly routines known as shellcode entirely inside active memory allocations. Because ubiquitous word-processing suites such as Microsoft Office are trusted implicitly by corporate administrative systems, adversaries target their native functionalities as primary operational vectors. Malicious actors frequently weaponize Visual Basic for Applications macros, Object Linking and Embedding vulnerabilities, and living-off-the-land system binaries to deliver compact, position-independent code directly into host processes. Once running, this position-independent code decouples itself from fixed execution offsets, undermining security perimeters and establishing covert administrative footholds.
Conventional memory defenses have developed structural limitations that leave systems vulnerable to sophisticated exploitation chains. System defenses such as Data Execution Prevention enforce a write-xor-execute restriction, ensuring allocated memory pages cannot simultaneously hold write permissions and execution rights. However, adversaries routinely bypass these constraints through code-reuse strategies, such as Return-Oriented Programming and Jump-Oriented Programming. These approaches assemble short, benign host instruction sequences terminating in return or indirect jump operations to execute arbitrary logic without introducing foreign executable memory blocks. Similarly, Address Space Layout Randomization scrambles the runtime base addresses of the operating system stack, heap, and executable shared libraries, yet memory disclosure defects or address leaks allow adversaries to calculate offset layouts and de-randomize the address map. While Control-Flow Integrity schemes verify execution paths against static transfer graphs, pragmatic trade-offs introduced to maintain software compatibility allow attackers to alter permissions using native system calls, transitioning seamlessly from code reuse to full payload execution.
To evade endpoint detection and response platforms, adversaries deploy sophisticated obfuscation schemes and runtime process injection strategies. The research team analyzed injection mechanisms including typical dynamic-link library injection, reflective library loading entirely from memory buffers, target thread execution hijacking, and portable executable injection via memory manipulation application programming interfaces such as VirtualAllocEx, WriteProcessMemory, and CreateRemoteThreadEx. Sophisticated payloads counter standard monitoring hooks by issuing direct kernel system calls, manually unhooking inspection libraries, and executing runtime application programming interface hashing through functions like LoadLibrary and GetProcAddress to hide function names. Furthermore, attackers utilize polymorphic encoders such as shikata_ga_nai, metamorphic instruction rewrites, chaotic encryption schemes, and intentionally low Shannon entropy code to defeat pattern-matching heuristics. A particularly complex vector evaluated by the authors is the Documents-inside-Documents technique, which coordinates multi-layered execution flows across nested documents, fileless macros, and process hollowing routines to blind traditional endpoint forensic sensors.
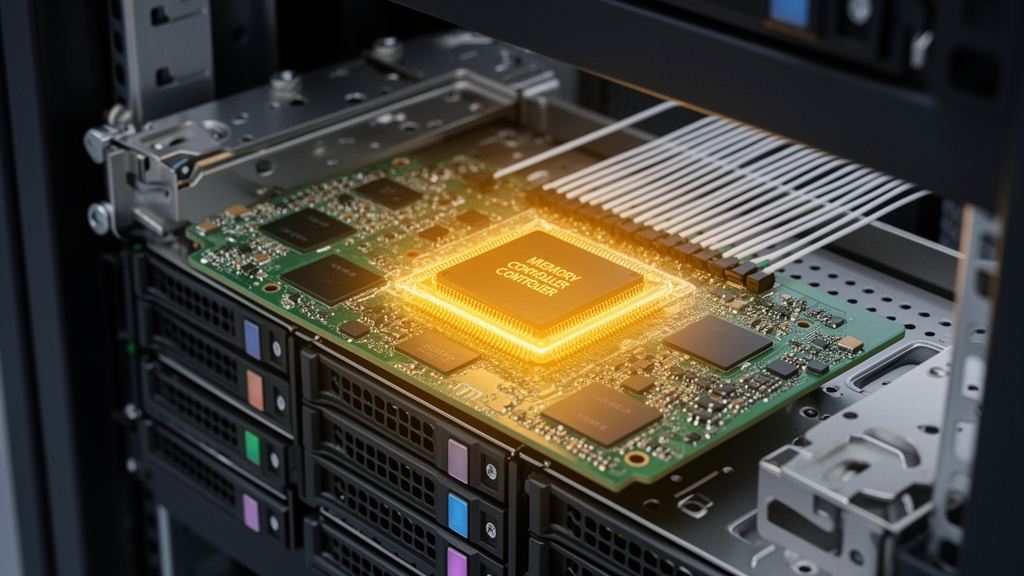
To counter these complex evasion pathways, the researchers designed FSMIGuard as a coordinated two-tier architecture operating across kernel-space and user-space boundaries. At the privileged system foundation, the framework deploys a kernel-mode hardware-assisted monitoring layer that interfaces with processor-level virtualization primitives, including Intel VT-x with extended page tables or ARM TrustZone technologies. This hardware interface intercepts raw memory allocations, monitors permission transitions, traces thread instantiation events, and transparently enforces write-xor-execute memory policies with negligible computational resistance. Simultaneously, an integrated user-mode profiling module continuously aggregates fine-grained telemetry concerning active memory region sizes, allocation quotas, and permission alterations within monitored applications like winword.exe. This raw structural data feeds into an advanced behavioral analysis engine and an anomaly scoring decision block. When confirmed anomalies exceed baseline threat thresholds, a kernel response module executes immediate automated countermeasures, such as process suspension, memory zeroing, memory quarantining, and comprehensive digital forensic telemetry capture for enterprise incident analysts.
The analytical core of the framework incorporates an algorithmic pipeline centered on a fine-tuned Transformer encoder model specifically trained to identify abnormal sequences of application programming interface calls. The Transformer features six encoder layers, a hidden dimension of 512 units, and eight multi-head self-attention mechanisms designed to track complex operational structures. Operating over a vocabulary dictionary of 2,500 unique Windows system identifiers, the network tokenizes observed runtime traces into padded sequences of 512 tokens. The model learns normal behavioral distributions from a training corpus of 35,000 legitimate sequences, with 7,500 sequences reserved for validation and 7,500 unseen payload traces utilized for evaluation. Optimized through the AdamW algorithm at an initial learning rate of 0.0001 with 0.01 weight decay over 50 epochs, the system continuously computes negative log-likelihood anomaly scores. Unfamiliar deviations in call sequences trigger proportional anomaly score escalations, flagging potential exploits before execution chains mature.
FSMIGuard supplements sequence tracking by deploying dynamic statistical thresholding alongside entropy and control-flow anomaly heuristics. Rather than enforcing rigid static alert thresholds that generate false alarms during normal enterprise computing spikes, the system models benign operational feature latencies using a multivariate Gaussian Mixture Model composed of four distinct mixture components. The model optimizes component weights and covariance matrices via Expectation-Maximization to establish dynamic anomaly criteria calibrated at 2.5 standard deviations above the distribution mean. Concurrently, an integrated byte evaluation module calculates the Shannon entropy of all newly allocated or modified executable memory regions. Benign runtime execution data typically reflects entropy values spanning from 3.8 to 6.2, whereas packed or encrypted malicious buffers consistently manifest entropy scores exceeding 6.2. These metrics are combined with dynamic control-flow graph verification to track indirect calls, returns, and jumps, generating a composite operational risk score across individual monitored endpoints.
The researchers conducted experimental validations within an enterprise testbed comprising 625 security-relevant host machines configured across virtualized VMware ESXi and VirtualBox environments. The heterogeneous platform included 248 enterprise workstations running Windows 10 version 22H2 build 19045.4780, four primary Domain Controllers executing Windows Server 2022 Standard within an Active Directory forest, and 289 modern Windows 11 endpoints. To evaluate defensive resilience across legacy infrastructure, the network incorporated 38 Windows 8 instances, 27 Windows 7 workstations, 14 Windows Vista platforms, and five legacy Windows XP systems. Physical hosts operated on standard Intel Core i7 and AMD Ryzen processors paired with 16 gigabytes of system memory. An isolated Kali Linux instance deployed across a bridged network segment executed attack simulations utilizing Metasploit, msfvenom, and custom payloads to generate polymorphic shellcode, chaotic encryption structures, macro exploits, and Documents-inside-Documents injection routines against target applications.
Quantitative evaluations demonstrated high diagnostic precision and statistical reliability across extensive simulated attack campaigns. In Receiver Operating Characteristic evaluations, the integrated API call sequence anomaly detector achieved an Area Under the Curve of 0.962, while the composite entropy and dynamic control-flow verification scoring system yielded an Area Under the Curve of 0.948. Bootstrapping validation incorporating 5,000 resamples across 1,000 randomized evaluation runs confirmed the statistical stability of these metrics. Across diverse attack vectors, FSMIGuard maintained consistent detection rates ranging between 87.4 percent and 91.0 percent. The framework preserved high discriminatory accuracy across diverse operating systems, keeping aggregate false-positive rates below 0.5 percent across mixed workstation subnets. In focused evaluations assessing Documents-inside-Documents payloads, the framework recorded an average precision of 90.40 percent alongside a tightly bounded false-positive rate of 1.21 percent, outperforming conventional single-layer inspection tools across multi-stage payload trials.
Hardware performance and operational scalability evaluations confirmed that the platform maintained a minimal footprint during sustained enterprise monitoring workloads. As the active endpoint monitoring infrastructure scaled from 50 to the full complement of 625 testbed nodes, processor overhead demonstrated a gradual linear increase that peaked at 4.2 percent CPU utilization under maximum operational load. Dedicated endpoint memory consumption remained minimal, registering an average overhead increase of 15.4 megabytes with a standard deviation of 2.1 megabytes per monitored host. When analyzing baseline processor activity during document handling, normal execution showed a stable low profile, whereas malicious payload execution provoked an immediate, sharp surge in CPU utilization across winword.exe processes. This sustained anomalous resource expenditure served as an effective supplementary behavioral signature, allowing the integrated system to differentiate legitimate background office tasks from fileless memory attacks without impairing end-user application responsiveness.
Controlled red-team penetration trials highlighted key tactical strengths along with ongoing engineering boundaries in memory-resilient defense orchestration. Across nineteen documented penetration attempts targeting Active Directory systems, file upload services, and command injection interfaces, the framework successfully blocked all five traditional macro-based phishing payloads. When confronted with five advanced Documents-inside-Documents vectors, four payloads initially achieved process footholds due to process hollowing techniques that manipulate application logic prior to startup; however, FSMIGuard successfully extracted forensic artifacts from two compromised hosts during runtime. The authors identified structural limitations, noting that kernel-level rootkits manipulating drivers remain capable of evading user-mode detection components. Consequently, future research initiatives will focus on extending hardware-assisted validation to non-Windows operating systems, developing predictive deep learning models to intercept exploits prior to memory execution, and formalizing mathematical verification protocols to guarantee control-flow integrity within processor virtualization layers.
Subject of Research: Hardware-assisted machine learning detection of in-memory shellcode execution
Article Title: Advanced detection technique for memory-resilient cyber attacks
Article References: Dora, J. R., Hluchý, L., Andok, R., & Agu, F. I. (2027). Advanced detection technique for memory-resilient cyber attacks. Cluster Computing, 30(1), Article 52. https://doi.org/10.1007/s10586-026-06763-w
Image Credits: AI Generated
DOI: 10.1007/s10586-026-06763-w
Keywords: FSMIGuard, in-memory attacks, shellcode detection, endpoint security, Transformer encoder, Gaussian Mixture Models, hardware-assisted monitoring, extended page tables, TrustZone, dynamic memory profiling, Shannon entropy, Documents-inside-Documents, code-reuse attacks, process injection, Win32 API, enterprise cybersecurity, kernel-mode protection
News Source: Denise Maddox. (November 21, 2026). Hardware Assisted Framework Detects Memory Resilient Attacks Across Enterprise Networks. Scienmag.