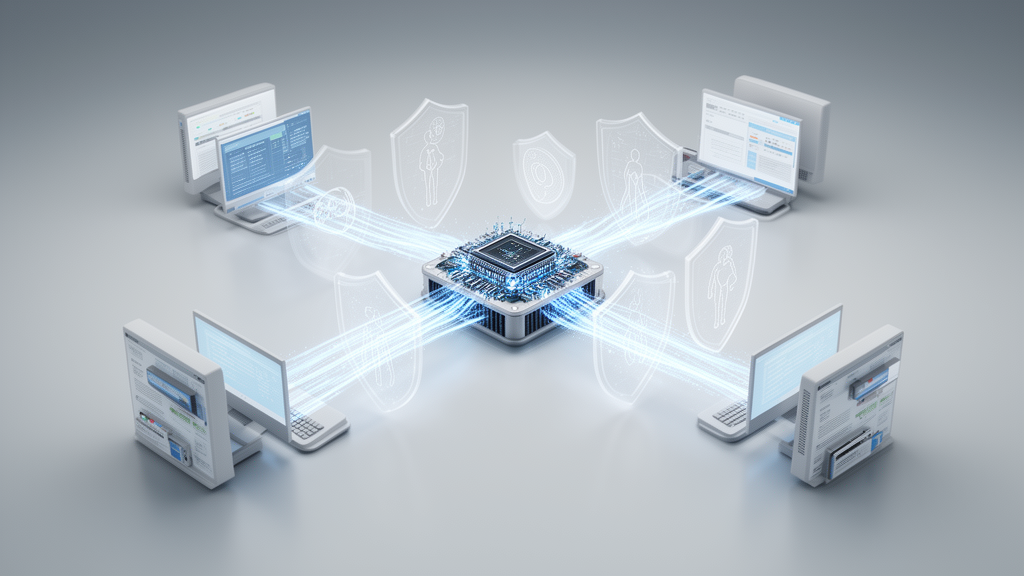
A newly proposed federated learning framework enables healthcare institutions to collaboratively train predictive models for diabetes diagnosis while keeping sensitive patient records private. Developed by researchers to overcome the strict data-sharing limitations of conventional centralized machine learning, the system, termed PrivFL-SMPC, allows institutions to perform distributed analytics on structured clinical datasets without exchanging raw patient data.
This data pooling creates significant privacy, security, and regulatory challenges that often prevent collaborative research across medical institutions.
Under the PrivFL-SMPC workflow, individual healthcare institutions begin by conducting comprehensive data preprocessing locally. This process includes data cleaning, normalization, and categorical encoding on local clinical datasets. Once the data preparation phase is complete, local predictive model training takes place directly on the participating institution’s internal infrastructure.
For local classification, the framework employs the LightGBM classifier. To improve predictive performance and computational efficiency during training, the researchers integrated an optimization technique called the Hybrid Red Kite–Runge Kutta Optimizer, designated as HKRO.
To safeguard the model updates that must be shared across the network to build a unified diagnostic tool, the system incorporates cryptographic defenses.
Alongside secret sharing, the architecture utilizes the Paillier cryptosystem to enable privacy-preserving secure aggregation. Through this cryptographic mechanism, participating institutions can collaboratively update and train a global diagnostic model without revealing raw patient records or intermediate model updates to external parties or coordinating servers.
In experimental evaluations using a diabetes dataset, the PrivFL-SMPC framework demonstrated strong predictive performance. The model achieved an overall accuracy of 0.9726, alongside a precision score of 0.97, a recall score of 0.96, and an F1-score of 0.96.
The experimental results show that the framework maintains high diagnostic accuracy while successfully preserving the confidentiality of model updates throughout the collaborative learning process. The authors report that the architecture offers an effective, scalable approach for privacy-preserving clinical analytics across distributed cloud infrastructures.
Subject of Research: Privacy-preserving federated learning for collaborative diabetes diagnosis
Article Title: PrivFL-SMPC: Privacy-aware federated learning using secure multi-party computation for collaborative diabetes diagnosis in the cloud
Article References: Raju, A. V., Naresh, V. S., & Rao, O. S. (2026). PrivFL-SMPC: Privacy-aware federated learning using secure multi-party computation for collaborative diabetes diagnosis in the cloud. Journal of Cloud Computing. https://doi.org/10.1186/s13677-026-00987-2
Image Credits: AI Generated
DOI: 10.1186/s13677-026-00987-2
Keywords: federated learning, secure multi-party computation, additive secret sharing, Paillier cryptosystem, diabetes diagnosis, LightGBM, Hybrid Red Kite Runge Kutta Optimizer, healthcare analytics, cloud computing, data privacy, machine learning, collaborative diagnosis, model aggregation, clinical datasets, predictive modeling
News Source: Veronica Carney. (November 19, 2026). Federated Learning Framework Diagnoses Diabetes Accurately While Protecting Patient Privacy. Scienmag.