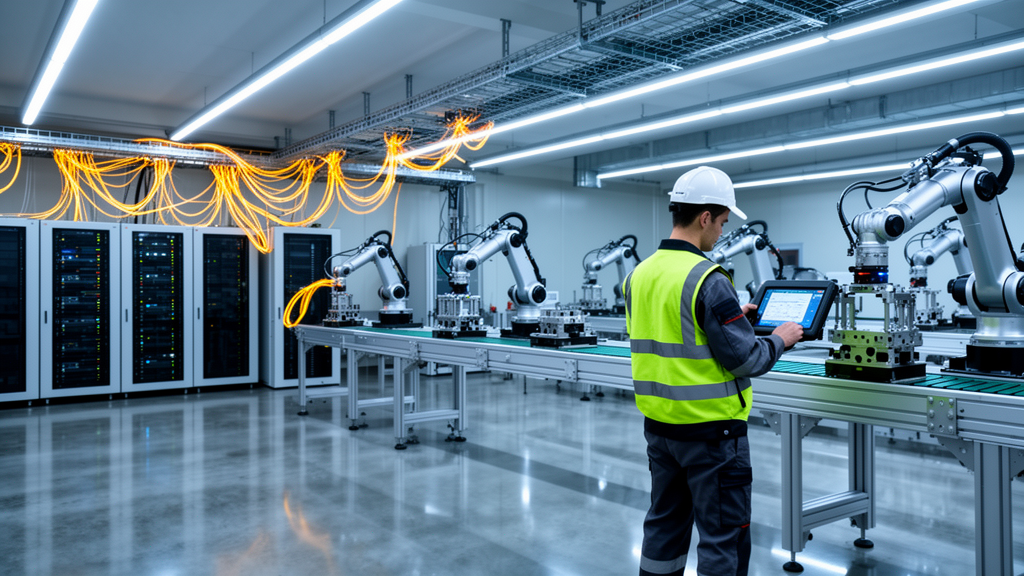
Modern industrial operations increasingly rely on multi-party collaboration across manufacturers, external suppliers, maintenance service providers, testing agencies, and regulatory platforms, requiring industrial data to leave local boundaries. To address the challenge of enforcing access consistency and confidentiality across independent administrative domains, researchers have developed a specialized data sharing scheme for the Industrial Internet of Things. Reported in the Journal of King Saud University Computer and Information Sciences, the framework pairs a compact weighted linear secret-sharing scheme access structure with a dual-channel consortium blockchain mechanism and version-bound edge-outsourced verification. The engineering team designed this unified cryptographic architecture to prevent revoked entities from accessing fresh production parameters while simultaneously lifting the bulk of the mathematical processing burden off constrained operational shop-floor terminals.
In practical Industrial Internet of Things environments, continuous streams of operational information, including sensor readings, process parameters, equipment health logs, and quality inspection metrics, must be selectively disclosed to external partners. Conventional ciphertext-policy attribute-based encryption allows a data owner to encrypt payloads under specific logical access formulas so that only users possessing qualifying credentials can recover the underlying symmetric key. However, standard deployments encounter significant operational friction when extended across organizational boundaries. Attribute significance in industrial facilities is rarely binary; factors such as job rank, organizational standing, machine trust levels, and task privileges carry disparate operational weights. When conventional attribute-based schemes attempt to model weighted policies, they typically rely on virtual-leaf node replication, duplicating leaf nodes according to raw integer weights and causing severe access-policy matrix expansion and ciphertext inflation.
To overcome this structural inefficiency without abandoning standard linear reconstruction, the authors designed a compact weighted linear secret-sharing scheme algorithm. The procedure normalizes candidate weights and access thresholds by computing the greatest common divisor across all attribute weights and the global access threshold. If any single normalized weight meets or exceeds the scaled threshold, the algorithm truncates it to the threshold, recognizing that the single attribute satisfies the authorization requirement and preventing redundant state evaluations. The method then employs dynamic programming to construct a monotone directed acyclic graph where states represent the monotone access conditions required to reach cumulative weight targets. By merging identical states and matching successor structures, the algorithm maps the policy into an access matrix whose row count is decoupled from the absolute sum of integer weights while preserving standard linear reconstruction properties.
Dynamic privilege revocation poses another fundamental barrier in collaborative industrial ecosystems, where employee roles shift, equipment configurations change, and supplier partnerships terminate. When privileges lapse, systems must ensure that historical cryptographic credentials cannot be combined with fresh network traffic to access updated files. The researchers addressed this by establishing a dual-channel collaborative revocation and update mechanism operating on a consortium blockchain. The architecture separates public on-chain coordination into an index-audit channel and a revocation-state channel. The index-audit channel records ciphertext version numbers, cryptographic digests, and content identifiers pointing to encrypted files stored in the InterPlanetary File System. Concurrently, the revocation-state channel publishes updated cryptographic state roots derived exclusively from the commitments of non-revoked users, completely decoupling version synchronization from identity verification.
When a revocation event occurs, such as following an identity invalidation, verified device anomaly, or key loss reported by an administrative domain, the certificate authority and attribute authority execute a synchronized protocol. The certificate authority removes the revoked participant from the active user registry, updates the system version secret, and recalculates a Merkle state root using the state commitments of the remaining authorized entities. New decryption key materials and membership witness paths are distributed exclusively to non-revoked users via secure private off-chain channels, while the updated state root is committed to the blockchain. Data owners re-encapsulate affected ciphertexts under the updated version secret and post new index records. Because revoked parties are excluded from the Merkle tree and receive no new version secrets, their retained legacy keys and historical proofs cannot satisfy the updated cryptographic masks.
To support resource-limited industrial devices, the system incorporates an edge-outsourced transformation protocol that delegates computationally intensive pairing operations to nearby edge servers. When an authorized data user initiates an access request, it generates a blinded transformation key using a local recovery secret that remains strictly confined to the terminal. The terminal then submits a non-revocation status proof binding its current state commitment, the latest confirmed on-chain state root, the active version number, and a fresh session nonce. The edge server verifies the non-revocation proof against the ledger, validates the session nonce to prevent replay attacks, confirms the integrity of the ciphertext retrieved from storage, and computes the partial decryption value. Crucially, the edge server cannot deduce the underlying plaintext or recovery secret from the blinded materials.
Because edge infrastructure may operate under untrusted, delayed, or adversarial conditions, the scheme introduces a strict verification check executed locally at the terminal before releasing plaintext data. The returned transformation package binds the partial decryption value directly to the version number, the on-chain ciphertext digest, and the request nonce. The data user verifies these values against the confirmed consortium ledger to detect stale or swapped results. The user then removes the blinding factor using its local recovery secret, computes the candidate encapsulation value, and calculates a key-confirmation tag. Only when this tag matches the tag stored in the verified ciphertext does the device derive the symmetric encryption key and decrypt the payload. In the event of an edge server timeout or verification failure, an authorized terminal retains the capability to execute complete local decryption as a resilient fallback.
The research team conducted extensive empirical evaluations to benchmark the performance and scaling behavior of the proposed protocol. The core cryptographic operations were developed in Go using the PBC library with Type A pairings over an elliptic curve setting, run within a virtualized Ubuntu testbed hosted on an Intel Core i7 processor. In comparative access-structure tests with attribute counts ranging from 10 to 60 and integer weights sampled between 1 and 5, the compact weighted linear secret-sharing scheme achieved access-structure compression ratios between 52.85% and 63.60% relative to virtual-leaf replication. This compression significantly lowered the dominant encryption cost by reducing the total number of matrix rows and associated ciphertext components, demonstrating efficiency gains over alternative weighted schemes such as RVWABE-CA while remaining comparable to SEWAC.
Computational cost assessments confirmed that shifting pairing operations to the edge provides dramatic efficiency gains for the end-user terminal during normal operations. While key-generation and data-encryption operations incurred minor overheads to bind random complementary values across user-version pairs, terminal-side final decryption required only a single target-group exponentiation, one group division, hash evaluations, and tag checks. The computational load at the user device remained essentially constant regardless of the number of attributes involved in policy reconstruction, contrasting sharply with fallback local decryption, which requires 2s plus 2 bilinear pairings for s reconstruction attributes. Further system tests using Hyperledger Caliper and containerized storage evaluated consortium blockchain read and write latencies across loads up to 1000 transactions per second, validating system stability under moderate concurrency.
Revocation and sharing latency analyses highlighted the operational trade-offs inherent in multi-party industrial deployment. By updating only a single Merkle state root rather than maintaining extensive linear revocation lists on-chain, the scheme constrained the growth of batch revocation latency as the volume of revoked users scaled from 10 to 400. In end-to-end access measurements, the complete operational pipeline proved slower than isolated cryptographic operations due to network retrieval and blockchain queries, yet terminal latency remained far less sensitive to policy complexity than un-outsourced architectures. The authors noted that current verification mechanics evaluate individual outsourced results sequentially rather than via batch proofs, and local containerized experiments do not fully reflect wide-area network jitter. Future investigations will examine dynamic trust metrics and metadata privacy preservation across broader distributed deployments.
Subject of Research: Cryptographic access control and dynamic revocation for cross-domain Industrial Internet of Things data sharing
Article Title: Cross-domain data sharing scheme for industrial IOT based on compact weighted access control and dynamic revocation
Article References: Yang, L., Tong, W., Chu, X., Jiang, W., & Li, Z. (2026). Cross-domain data sharing scheme for industrial IOT based on compact weighted access control and dynamic revocation. Journal of King Saud University Computer and Information Sciences, 38(10), Article 1032. https://doi.org/10.1007/s44443-026-01428-5
Image Credits: AI Generated
DOI: 10.1007/s44443-026-01428-5
Keywords: Industrial Internet of Things, CP-ABE, access control, data sharing, consortium blockchain, linear secret sharing scheme, dynamic revocation, outsourced decryption, edge computing, IPFS, cryptographic protocols, state commitments, cross-domain collaboration, information security, attribute-based encryption, data confidentiality, bilinear pairings, Merkle tree
News Source: Denise Maddox. (November 19, 2026). Compact Access Scheme Secures Cross Domain Industrial Internet Data Sharing. Scienmag.