A systematic review of 128 eligible peer-reviewed studies found that poisoning-resilient federated learning in the Internet of Medical Things depends on layered defenses that balance privacy, attack detection, energy use, communication overhead and real-time performance. The review synthesizes evidence published from January 2022 through October 2025 and maps major threats—including data and model poisoning, backdoors, Byzantine and Sybil behavior, gradient leakage, intrusion and communication attacks—to proposed cross-layer responses.
The Internet of Medical Things, or IoMT, includes interconnected hospital equipment, wearables and implantable devices that can support real-time monitoring, remote diagnosis and data-driven clinical decisions. Its distributed architecture increases exposure to threats across devices, communication links, aggregation servers and stored data. Resource-constrained and heterogeneous devices can also be vulnerable to adversarial manipulation, denial-of-service and poisoning attacks. Federated learning reduces the need to centralize sensitive medical records: participating nodes train locally and exchange model updates or gradients for aggregation, although that exchange creates additional security challenges.
The authors searched IEEE Xplore, the ACM Digital Library, Scopus, Web of Science, PubMed/MEDLINE, ScienceDirect, Google Scholar and DBLP, applying PRISMA 2020 principles. They screened 847 records, removed duplicates to leave 407, assessed 221 full-text articles and synthesized 128 studies that met the criteria for IoMT-specific poisoning, anomaly-detection or intrusion-detection research with empirical analysis. The mixed-method synthesis summarized detection accuracy, false-positive rate, latency, computational overhead and other performance measures while thematically comparing architectures, attack types and detection techniques.
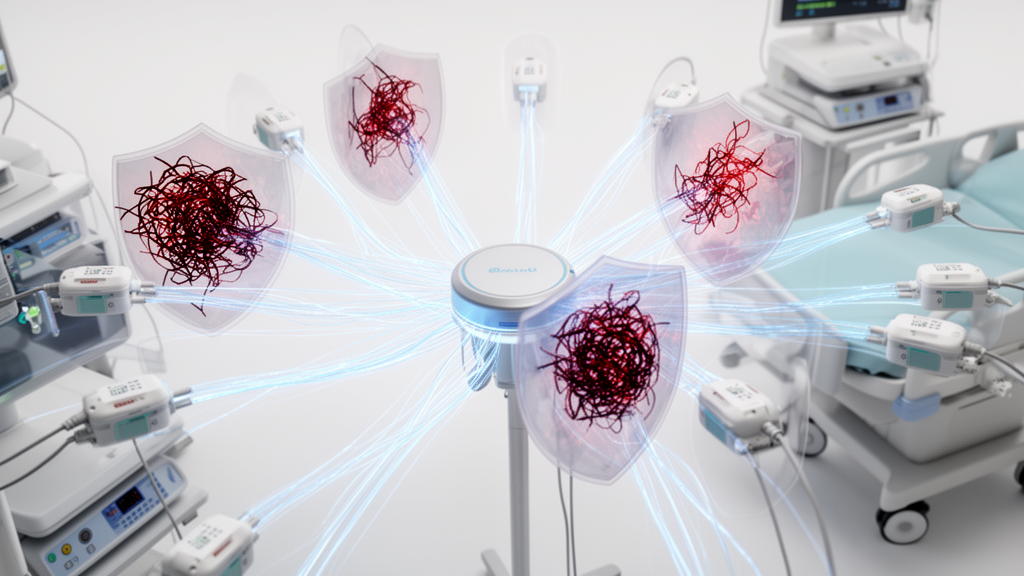
The resulting taxonomy separates data poisoning, in which training samples or labels are manipulated, from model poisoning, in which malicious parameters or learning procedures directly affect aggregation. Dirty-label and clean-label attacks belong to the data-poisoning category; label flipping is a representative example. Backdoor attacks insert hidden triggers that can make a global model behave maliciously when the trigger appears. Byzantine clients submit inconsistent updates, while Sybil attacks give one adversary influence over multiple identities. The review also considers intrusion-based attacks that compromise sensors, gradient-leakage and inference attacks, and communication threats that can capture, delay or alter updates in transit.
Proposed defenses operate at different layers. Robust aggregation methods, including Krum, Multi-Krum, Trimmed Mean and Median, are intended to isolate anomalous updates. Anomaly-based intrusion detection evaluates client behavior, while differential privacy adds calibrated noise to updates and cryptography conceals their contents. Blockchain-enabled federated learning can add integrity checks, consensus and traceability. The review emphasizes hybrid and hierarchical strategies rather than treating any single mechanism as universally effective, because each approach addresses a different part of the attack surface.
The synthesis identifies a central trade-off between privacy and poisoning detection. Differential privacy can make abnormal update patterns harder to recognize, while homomorphic encryption and secure multi-party computation impose substantial computational and communication costs. A study cited by the review reported approximately 17–18 seconds per training round when encryption, local training and blockchain consensus were combined, a delay described as acceptable for offline analysis but unsuitable for real-time applications. Blockchain protocols may also add communication rounds, storage requirements and latency, while strong aggregation rules can be less effective against coordinated or stealthy attacks in highly non-IID medical data.
Resource limits make these trade-offs particularly important for wearables and implantables, which have constrained battery life, memory and processing capacity. Strong cryptographic operations, complex aggregation and repeated verification may consume more energy than such devices can sustain. Hierarchical edge-fog-cloud arrangements, local edge verification and lightweight hybrid defenses may help by detecting suspicious updates before global aggregation and limiting the propagation of compromised contributions, but the reviewed evidence does not establish one universally deployable configuration for clinical use.
The evidence base also has important limitations. Many cited evaluations used controlled laboratory settings, stable communication, synchronized participation and relatively simple assumptions about adversaries. Common benchmarks such as MNIST, FMNIST and CIFAR-10 are clean, balanced image datasets that do not represent the multimodal, noisy, temporally correlated and highly non-IID data produced by clinical systems. The review notes that medical datasets are often restricted by privacy rules, while synthetic imbalance and limited-scale or outdated datasets further restrict reproducibility. Results above 90% accuracy reported under such conditions therefore do not by themselves demonstrate robustness, scalability or readiness for hospital deployment.
Based on the reviewed evidence, the authors call for evaluations that incorporate heterogeneous devices, packet loss, dropout, delayed updates, realistic poisoning scenarios and diverse healthcare data, including multimodal sensor and electronic-health-record streams. Other priorities include lightweight cryptography, explainable rejection of suspicious updates, auditable records, adaptive privacy budgets and dynamic defense thresholds. The review presents these as research directions derived from the literature, not as clinically validated protections. Its overall conclusion is that secure federated medical IoT requires coordinated safeguards across device, communication, aggregation and decision layers, with security gains weighed against energy consumption, latency, convergence stability and regulatory requirements.
Subject of Research: Systematic review of poisoning threats and defenses in federated learning for the Internet of Medical Things
Article Title: Poisoning resilient federated learning for secure internet of medical things a systematic review
Article References: Unbreen, A., Naeem, H., Hassan, S. R., & Hassan, A. S. (2026). Poisoning resilient federated learning for secure internet of medical things a systematic review. Discover Artificial Intelligence, 6(1), Article 1278. https://doi.org/10.1007/s44163-026-02344-3
Image Credits: AI Generated
DOI: 10.1007/s44163-026-02344-3
Keywords: federated learning, Internet of Medical Things, poisoning attacks, robust aggregation, differential privacy, intrusion detection, blockchain security, healthcare cybersecurity, non-IID data, systematic review, Poisoning, resilient
News Source: Veronica Carney. (October 20, 2026). Systematic review maps poisoning threats and layered defenses in federated learning for medical IoT. Scienmag.