• HOME
  • NEWS
  • EXPLORE
    • CAREER
      • Companies
      • Jobs
    • EVENTS
    • iGEM
      • News
      • Team
    • PHOTOS
    • VIDEO
    • WIKI
  • BLOG
  • COMMUNITY
    • FACEBOOK
    • INSTAGRAM
    • TWITTER
Tuesday, October 20, 2026
BIOENGINEER.ORG
No Result
View All Result
  • Login
  • HOME
  • NEWS
  • EXPLORE
    • CAREER
      • Companies
      • Jobs
        • Lecturer
        • PhD Studentship
        • Postdoc
        • Research Assistant
    • EVENTS
    • iGEM
      • News
      • Team
    • PHOTOS
    • VIDEO
    • WIKI
  • BLOG
  • COMMUNITY
    • FACEBOOK
    • INSTAGRAM
    • TWITTER
No Result
View All Result
Bioengineer.org
No Result
View All Result
Home NEWS Science News Technology

Federated framework detects email malware in benchmarks under non-IID data

by
October 20, 2026
in Technology
Reading Time: 2 mins read
0
Federated framework detects email malware in benchmarks under non-IID data

Federated framework detects email malware in benchmarks under non-IID data

Share on FacebookShare on TwitterShare on LinkedinShare on RedditShare on Telegram

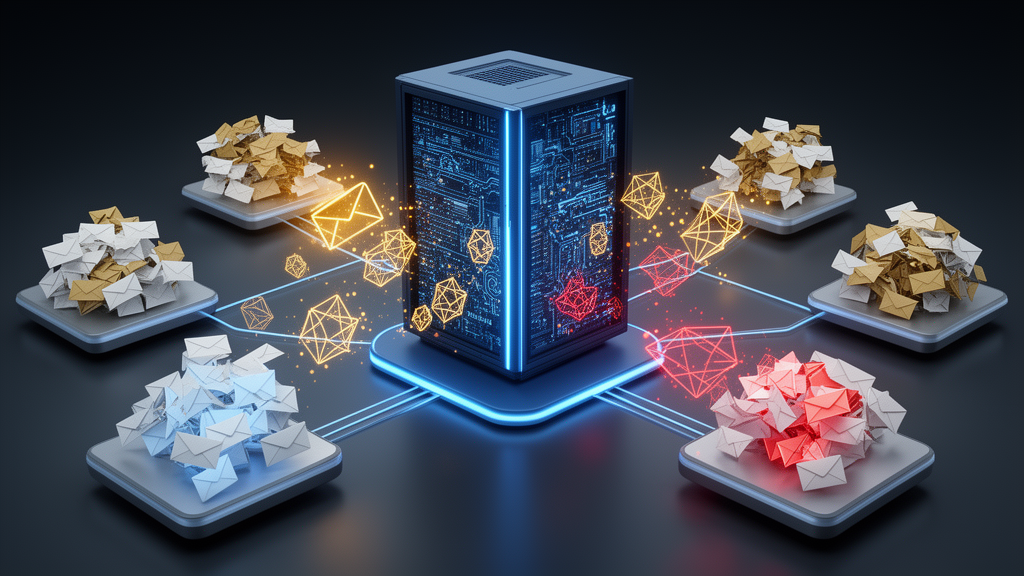
A computational framework designed to detect malware in email attachments while keeping data distributed across participating clients achieved 95.75% accuracy and a 94.33% F1-score under non-independent and identically distributed benchmark conditions, according to a study published in Neural Computing and Applications . The system, called HEFL-MD, recorded 96.70% accuracy and a 95.53% F1-score under IID conditions. These results came from experiments using publicly available benign and malware datasets rather than a live enterprise email environment.

Malicious attachments exchanged through enterprise and cloud-based communication platforms remain a significant malware-distribution route. Deep-learning approaches can provide strong detection capability, but centralized training raises privacy, scalability, and deployment concerns when email data are distributed among separate organizations. The proposed framework instead trains a shared visual-learning model across clients without transferring their underlying data to one central location.

Its principal technical problem is statistical heterogeneity: conventional federated-learning methods can lose performance when client data distributions are non-IID, producing client drift and less stable model updates. HEFL-MD addresses this instability with an aggregation strategy that adaptively re-weights client updates according to model divergence. The researchers evaluated the system against Federated Averaging, FedProx, and SCAFFOLD and reported approximately 3–5% higher F1-scores, together with more stable convergence under non-IID data distributions.

These are comparative findings from the tested experimental settings, not evidence that every federated detector will behave in the same way. The framework also includes an explainability component that produces visual explanations for malware predictions. The study abstract describes these outputs as meaningful, but the accessible source material does not specify their resolution, structure, or any user evaluation.

HEFL-MD also narrowed the reported performance gap between federated and centralized training to approximately 1–2%. Together, the results suggest that the tested distributed approach retained most of the centralized model’s performance while producing visual explanations, but the experiments do not constitute a comprehensive assessment of privacy leakage or the framework’s effectiveness against newly encountered email campaigns. Within those limits, the study provides a benchmark-level demonstration of heterogeneity-aware aggregation for email-attachment malware classification.

The authors present the method as scalable, privacy-preserving, and interpretable for distributed email-security applications. Because the evidence presented here comes from publicly available datasets and computational experiments, further validation would be needed to establish performance in operational enterprise settings or against live malware activity.

Subject of Research: Federated visual learning for benchmark email-attachment malware detection under non-IID client data

Article Title: A heterogeneity-aware federated explainable visual learning framework for robust email malware detection

Article References: Shanmuga Priya, G., Mani, V. R. S., & Chellaswamy, C. (2026). A heterogeneity-aware federated explainable visual learning framework for robust email malware detection. Neural Computing and Applications, 38(20), Article 821. https://doi.org/10.1007/s00521-026-12523-z

Image Credits: AI Generated

DOI: 10.1007/s00521-026-12523-z

Keywords: email malware, federated learning, visual classification, non-IID data, client drift, explainable AI, malware detection, model aggregation, privacy-preserving AI, heterogeneity-aware, federated, explainable

News Source: Blake Davidson. (October 20, 2026). Federated framework detects email malware in benchmarks under non-IID data. Scienmag.
Tags: client driftemail malwareExplainableExplainable AIfederatedfederated learningheterogeneity-awaremalware detectionmodel aggregationnon-IID dataprivacy-preserving AIvisual classification
Share12Tweet7Share2ShareShareShare1

Related Posts

Voltage-controlled lithium niobate chip advances compact full-color laser displays

Voltage-controlled lithium niobate chip advances compact full-color laser displays

October 20, 2026
NiTe–MoS2/rGO electrode reaches 782 farads per gram in laboratory testing

NiTe–MoS2/rGO electrode reaches 782 farads per gram in laboratory testing

October 20, 2026

Particle Sensor Preceded HCl Detector in One Simulated PVC Trench Test

October 20, 2026

Rosario R package tests temporal overlap in British Columbia cervids

October 20, 2026

POPULAR NEWS

  • Ultrafast switching of optical properties in a doped semiconductor by intense femtosecond laser pulses

    Ultrafast switching of optical properties in a doped semiconductor by intense femtosecond laser pulses

    29 shares
    Share 12 Tweet 7
  • Federated framework detects email malware in benchmarks under non-IID data

    29 shares
    Share 12 Tweet 7
  • Association between CISD2 expression and clinicopathological features and prognosis in gastric cancer: a systematic review, meta-analysis, and database validation

    29 shares
    Share 12 Tweet 7
  • First stygobiotic Garra rufa found beside Iranian cave fish

    29 shares
    Share 12 Tweet 7

About

We bring you the latest biotechnology news from best research centers and universities around the world. Check our website.

Follow us

Recent News

Ultrafast switching of optical properties in a doped semiconductor by intense femtosecond laser pulses

Federated framework detects email malware in benchmarks under non-IID data

Association between CISD2 expression and clinicopathological features and prognosis in gastric cancer: a systematic review, meta-analysis, and database validation

Subscribe to Blog via Email

Enter your email address to subscribe to this blog and receive notifications of new posts by email.

Join 85 other subscribers
  • Contact Us

Bioengineer.org © Copyright 2023 All Rights Reserved.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In
No Result
View All Result
  • Homepages
    • Home Page 1
    • Home Page 2
  • News
  • National
  • Business
  • Health
  • Lifestyle
  • Science

Bioengineer.org © Copyright 2023 All Rights Reserved.